















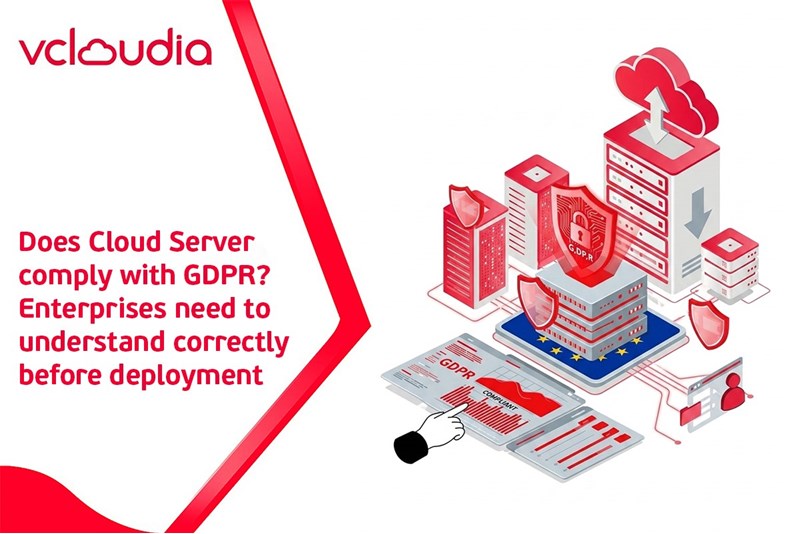
Does Cloud Server comply with GDPR? Enterprises need to understand correctly before deployment
May 29, 2026In the digital transformation process, Cloud Server is becoming a popular infrastructure platform for many enterprises thanks to its flexibility, fast scalability, and optimal costs. However, along with the use of Cloud, a major question is frequently raised: Does Cloud Server comply with GDPR? This article by Vcloudia will help you answer this question, while pointing out common risks and how to properly deploy Cloud so that enterprises can operate safely and sustainably.
What is GDPR?
GDPR (General Data Protection Regulation) is the General Data Protection Regulation of the European Union, which officially came into effect on May 25, 2018. This is considered one of the strictest legal frameworks in the world regarding privacy and personal data protection. GDPR was created to address the reality that personal data is increasingly collected, processed, and circulated widely in the digital environment, especially on the Internet and global technology platforms.
The core objective of GDPR is to hand back control of personal data to users, while forcing organizations and enterprises to be transparent and accountable throughout the entire data processing lifecycle, from collection, storage, and usage to deletion. According to GDPR, personal data does not only stop at familiar information such as full name, email, or phone number, but also includes IP addresses, cookies, location data, online behavior, and even biometric data.
An important point that is often misunderstood is that GDPR does not only apply to enterprises headquartered in the EU. In fact, any organization that provides products or services to EU citizens or collects and processes the personal data of EU citizens must comply with GDPR, regardless of whether that enterprise operates in Vietnam or any other country.
Does Cloud Server comply with GDPR?
Cloud Server can absolutely comply with GDPR, but this does not happen automatically or by default. GDPR does not prohibit enterprises from using Cloud Server, and in reality, the majority of organizations in Europe, from startups to multinational corporations, operate their systems on the Cloud platform. What GDPR is concerned about is not whether an enterprise uses Cloud or On-premise, but whether the enterprise can truly control personal data.
Cloud Server is essentially just infrastructure. Whether a Cloud system complies with GDPR or not depends on many factors, including the Cloud provider, how the enterprise configures and operates the system, as well as the established personal data processing procedures. GDPR clearly delineates the roles between Data Controller and Data Processor. The enterprise, acting as the Data Controller, remains the party ultimately responsible for personal data, even when the data is processed on a third-party's Cloud infrastructure. The Cloud provider merely plays the role of Data Processor and is responsible within the scope of the infrastructure they provide.
Conditions for Cloud Server to achieve GDPR compliance
For a Cloud Server system to substantively comply with GDPR, enterprises must simultaneously ensure multiple conditions related to legality, technology, and operations, rather than just stopping at choosing a provider.
Data storage location (Data Location & Data Residency)
GDPR requires that the personal data of EU citizens must be stored and processed in EU member states or countries recognized by the EU as having an adequate level of data protection. In the event that data is transferred outside the EU, the enterprise must have a lawful data transfer mechanism, such as Standard Contractual Clauses (SCC) or Binding Corporate Rules (BCR).
In a Cloud environment, this requirement directly relates to the selection of regions and zones, as well as how auxiliary services like backup, logging, or disaster recovery are configured. A fairly common mistake is that enterprises only pay attention to the primary server location, but fail to control whether backup or log data is stored in regions outside the EU.
Data processing contracts and commitments (DPA)
GDPR makes it mandatory to have a Data Processing Agreement (DPA) between the Data Controller and the Data Processor. The DPA is a legal document that clearly specifies the scope of data processing, purpose of use, security responsibilities, support obligations during incidents, and how to handle data upon contract termination. If the Cloud provider does not have a DPA or the DPA does not fully meet GDPR requirements, that Cloud system cannot be considered GDPR-compliant, no matter how modern its technical infrastructure is.
Data security on Cloud Server
Data security is one of the most important pillars of GDPR. Cloud Server needs to support security mechanisms such as data encryption at rest and in transit, granular access authorization, as well as comprehensive logging of data access and processing behaviors. However, the Cloud only provides the tools. Whether the configuration is right or wrong, whether unauthorized access can be detected, and whether the requirement to report incidents within 72 hours can be met, all depend on how the enterprise operates the system.
The ability to control and delete personal data
GDPR grants users very strong rights, especially the right to access, rectify, and delete personal data. Therefore, the Cloud Server system must allow the enterprise to pinpoint exactly where personal data is located, control the data lifecycle, and thoroughly delete data upon request. If data still exists in backups, caches, or logs without being completely erasable, the enterprise will face many difficulties in complying with GDPR.
Common risks that cause Cloud systems to fail GDPR compliance
Storing data in the wrong geographical region
Many enterprises violate GDPR unintentionally by selecting default regions, failing to check the storage locations of auxiliary services, or using analytics tools and CDNs located outside the EU. Transferring personal data outside the EU without a lawful mechanism is a serious violation of GDPR.
Lack of DPA contracts or GDPR clauses
Another risk arises from enterprises using the Cloud without signing a DPA, not carefully reading the data processing clauses, or not clearly knowing which sub-processors the provider uses. This causes the enterprise to lose legal control over the data.
Incorrect Cloud configuration leading to data exposure
The majority of data leak incidents on the Cloud stem from configuration errors, such as leaving storage public, unauthenticated APIs, or overly broad access permissions. GDPR does not accept technical excuses when personal data is exposed.
Inability to control the personal data lifecycle
Allowing personal data to exist for too long without being deleted when its purpose of use has expired is one of the common violations. The Cloud does not automatically solve this problem if the enterprise does not establish clear data management procedures.
What do enterprises need to do to use Cloud Server in compliance with GDPR?
To use Cloud Server in proper compliance with GDPR, enterprises need to approach the issue holistically. This includes clearly identifying the Data Controller role, selecting a Cloud provider with transparent GDPR commitments, signing a comprehensive DPA, and designing a Cloud architecture according to the privacy-by-design principle. Besides that, enterprises also need to control the personal data lifecycle and train their technical and operational teams to correctly understand GDPR. GDPR is not a barrier to the Cloud. On the contrary, it is a measure of an enterprise's maturity in managing data responsibly and sustainably.
Conclusion
Cloud Server can comply with GDPR, but it does not automatically comply with GDPR. Compliance depends on how the enterprise selects providers, configures infrastructure, and manages personal data. Instead of fearing GDPR, enterprises should view this as an opportunity to standardize systems, enhance security, and build trust with customers. A Cloud system deployed in true compliance with GDPR not only helps avoid legal risks but also creates a long-term competitive advantage.
Vcloudia Cloud Server – The Cloud You Can Count On
If you're concerned about the potential limitations of Cloud Servers, Cloud server by Vcloudia is a reliable solution for businesses of all sizes. With a modern infrastructure and comprehensive customer support, Vcloudia delivers a cloud experience with:
- Powerful connectivity to ensure stable 24/7 access
- Advanced security standards, compliant with international certifications such as ISO 27001:2013, ISO 20000:2018, ISO 9001:2015
- Flexible pricing packages tailored to your specific business needs
- Expert technical support, making migration and system deployment fast, safe, and compatible
Contact information:
- Hotline: +855 888 55 66 08 (free of charge)
- Fanpage: https://www.facebook.com/vcloudia/
- Website: https://vcloudia.com
Featured news
Related news
What is a Snapshot? The Difference Between Snapshot and Backup
Snapshot is a familiar concept in data management and protection. In the context of the information technology boom, where data is a major asset for businesses, understanding Snapshots as well as their application is a key factor for enterprises to maximize technological efficiency.
What is a Firewall? The Role and Importance of Firewalls for Users
In the context of ever-increasing cyberattacks, system security has become a top priority for many enterprises. Alongside deploying antivirus software and controlling connection ports, firewalls are also considered a key solution to effectively enhance cybersecurity.
What is DDoS? Signs, Mitigation Strategies, and Effective Prevention
DDoS is a highly dangerous cyberattack that leaves severe consequences for enterprises. Therefore, gaining a clear understanding of DDoS attacks, as well as how to detect and prevent them, is a topic of significant interest to many.
What is a Trojan? How to Detect, Avoid, and Prevent It
A Trojan is a type of malicious code or software that can cause severe consequences to computer operations. So, what is a Trojan? How can you prevent a Trojan from infiltrating your computer? In the following article, Vcloudia will provide detailed information on these issues.
What is Cloud Backup? Classification, benefits, and limitations
Cloud Backup is a solution that plays an important role in backing up and recovering data when an incident occurs. So what exactly is Cloud Backup? Let's find out the details with Vcloudia in the following article.
What is Cloud Storage? Features and Benefits of Using It
Cloud Storage is the perfect storage solution alternative to bulky, space-consuming physical hard drives. So, what is Cloud Storage? Let's explore the details with Vcloudia through the following article.
What is an API? Characteristics and applications in website design
API, short for Application Programming Interface, is a concept no longer unfamiliar in the information technology field. So what exactly is an API and why is it so important? Let's find out with Vcloudia.
What is Node.js? Instructions on how to install Node.js on cPanel
Currently, it is easy to see that Node.js is being used by quite a lot of people. This is because Node.js can support users in running on multiple platforms and multiple devices.
What is Vultr VPS? Should you use Vultr VPS?
Vultr VPS is one of the best cloud storage solutions in the world. In this article, you will learn the concept: "What is Vultr VPS?", as well as understand its advantages and disadvantages.
Zoom Cloud Meeting: What is it? Basic Things You Should Know About Zoom Cloud Meeting
In 2020, Zoom Cloud Meeting became one of the leading video conferencing software applications. It allows you to virtually interact with colleagues when in-person meetings aren't possible, and it has also been very successful for social events.